Code & Configuration Reviews
Review a defined part of your code or setup.
Ask about a bounded review of a repository, feature or configuration. We agree the checks, reviewer and deliverable before quoting the work.
Discuss a reviewWhat to tell us
Tell us which part of the system concerns you and what you need to decide. The review proposal identifies the relevant code or settings, the access needed and the findings you will receive.
Related note: What to agree before a code review
Reference videos
Third-party visual references from 13G. These are layout examples, not work delivered by Drevhe.
Secoya
13G design referenceWeem
13G design referenceLemlist
13G design referenceLaGrowthMachine
13G design referenceA review with clear boundaries
Scope
Name the repository, feature or configuration area and the questions the review should answer.
Context
Understand how the software is used and what the relevant access rules are meant to allow.
Checks
Agree the review method and relevant checks for the language, framework and system involved.
Findings
Receive a written record of the issues found, their evidence and suggested next steps.
Limits
See what was examined, what was excluded and where more investigation is needed.
Follow-up
Scope any fixes and rechecks separately, with responsibility for each change agreed in advance.
What can a review cover?
A defined area such as an application's access checks, dependency setup or deployment configuration. We confirm relevant review experience and access before accepting a scope. Some projects need a specialist assessor.
Can we commission a review of code you did not write?
Yes, subject to a scope and fit check. Share the technology and the question you need answered. We agree permission, access, the reviewer and the findings report before starting.
Is this a penetration test or a compliance assessment?
No. This offer is a bounded code or configuration review. Penetration testing, certification assessments and regulatory compliance opinions require a separately qualified provider and engagement.
Do you provide incident response or continuous monitoring?
We do not offer incident response, a security operations centre or continuous threat monitoring. This page covers planned review work with an agreed scope and delivery date.
Does a review guarantee the system is secure?
A review reports what was found within the agreed scope and access. It cannot establish that every vulnerability has been found. The report states its coverage and limitations.
Can you fix the issues you find?
We can quote fixes that fall within our delivery competence. Remediation and rechecking are defined separately so you can decide what to approve and who should carry it out.
How is a review priced?
We quote after identifying the code or configuration, the review questions and the relevant reviewer. The proposal specifies the findings report, exclusions and any follow-up included.
Website concepts
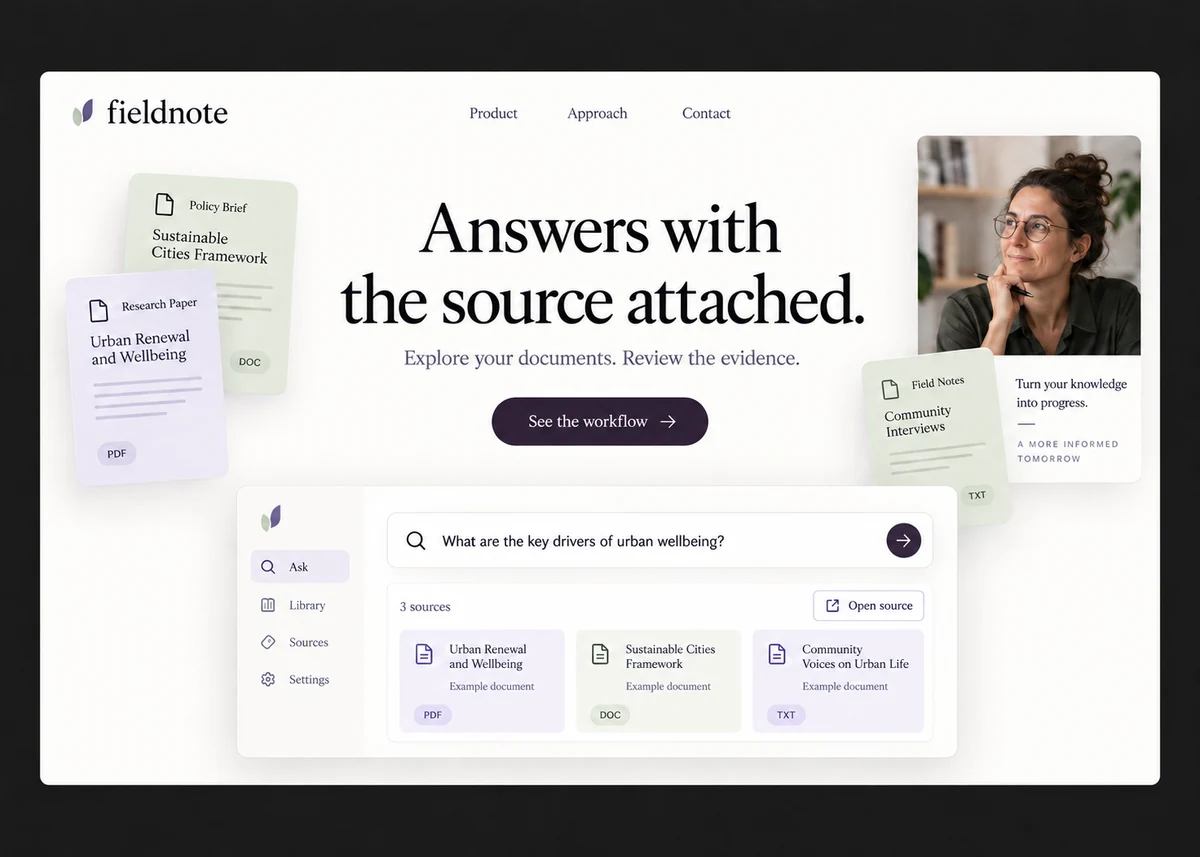
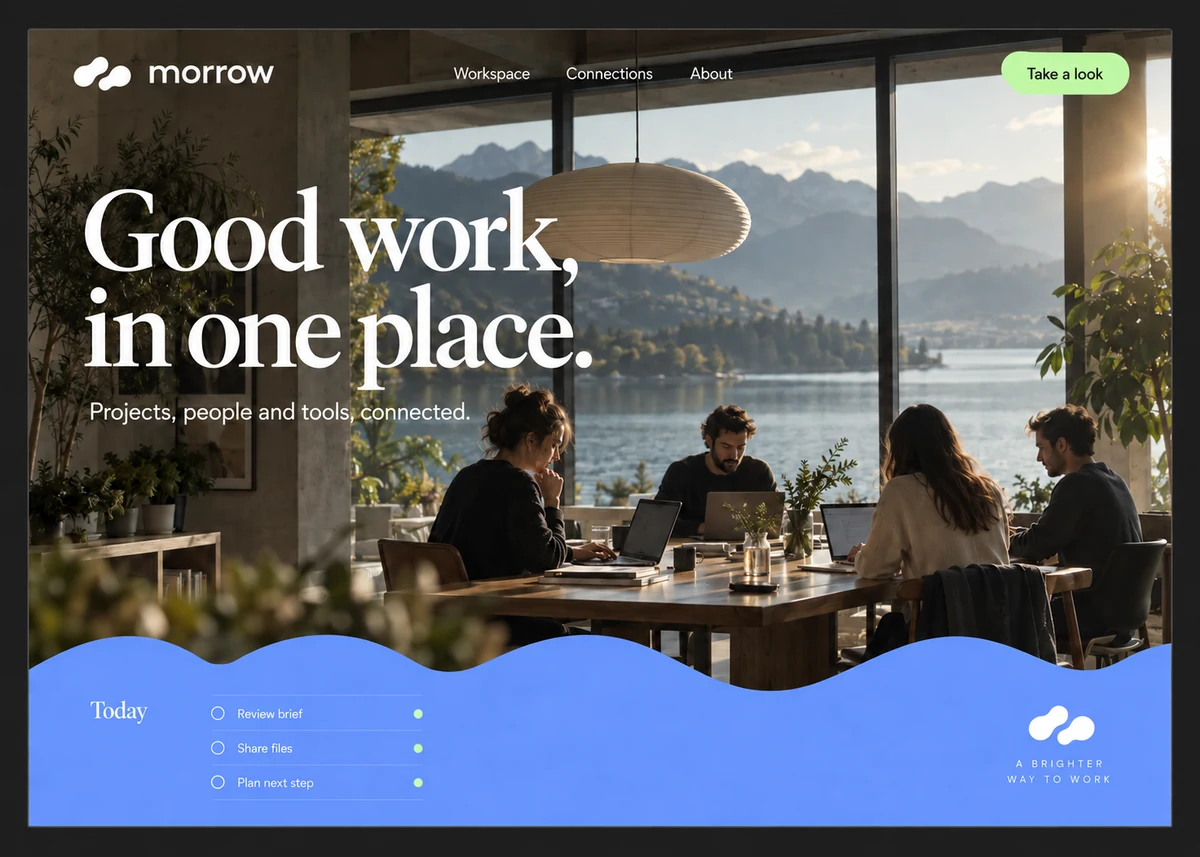
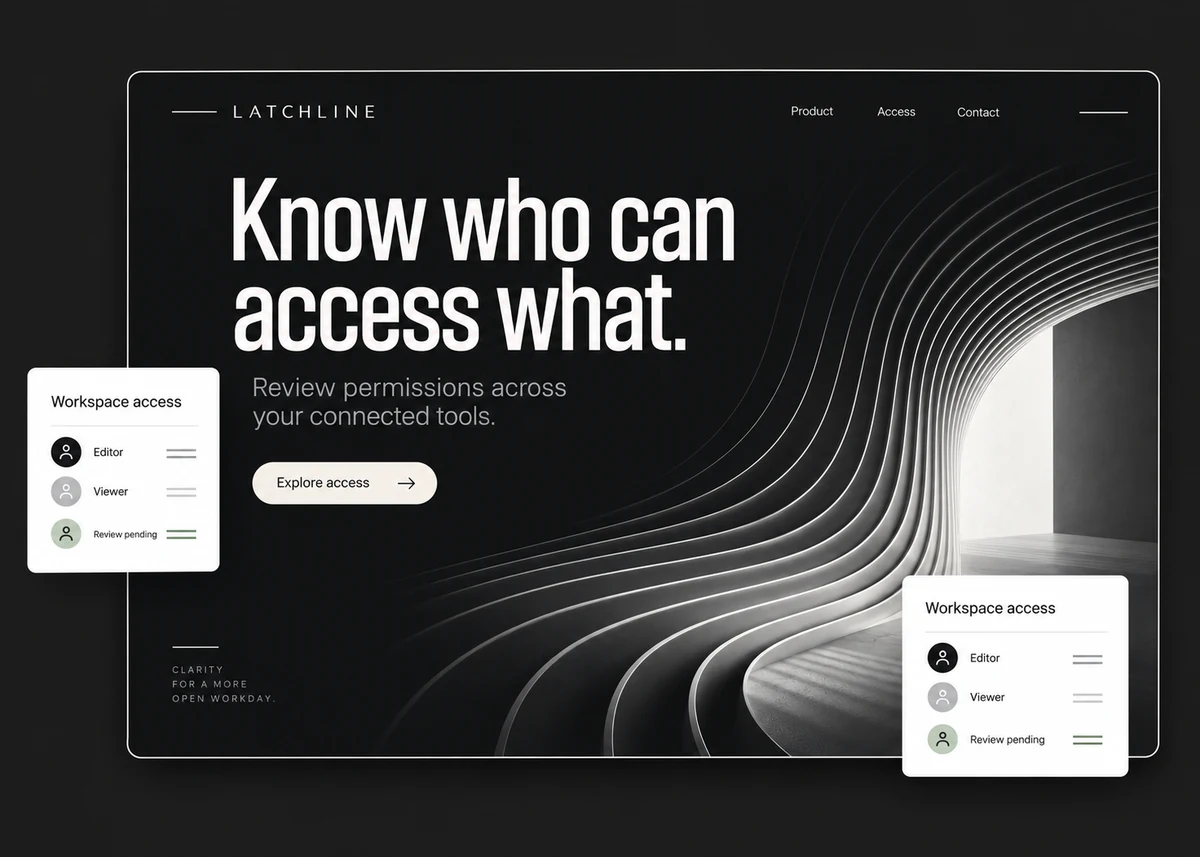
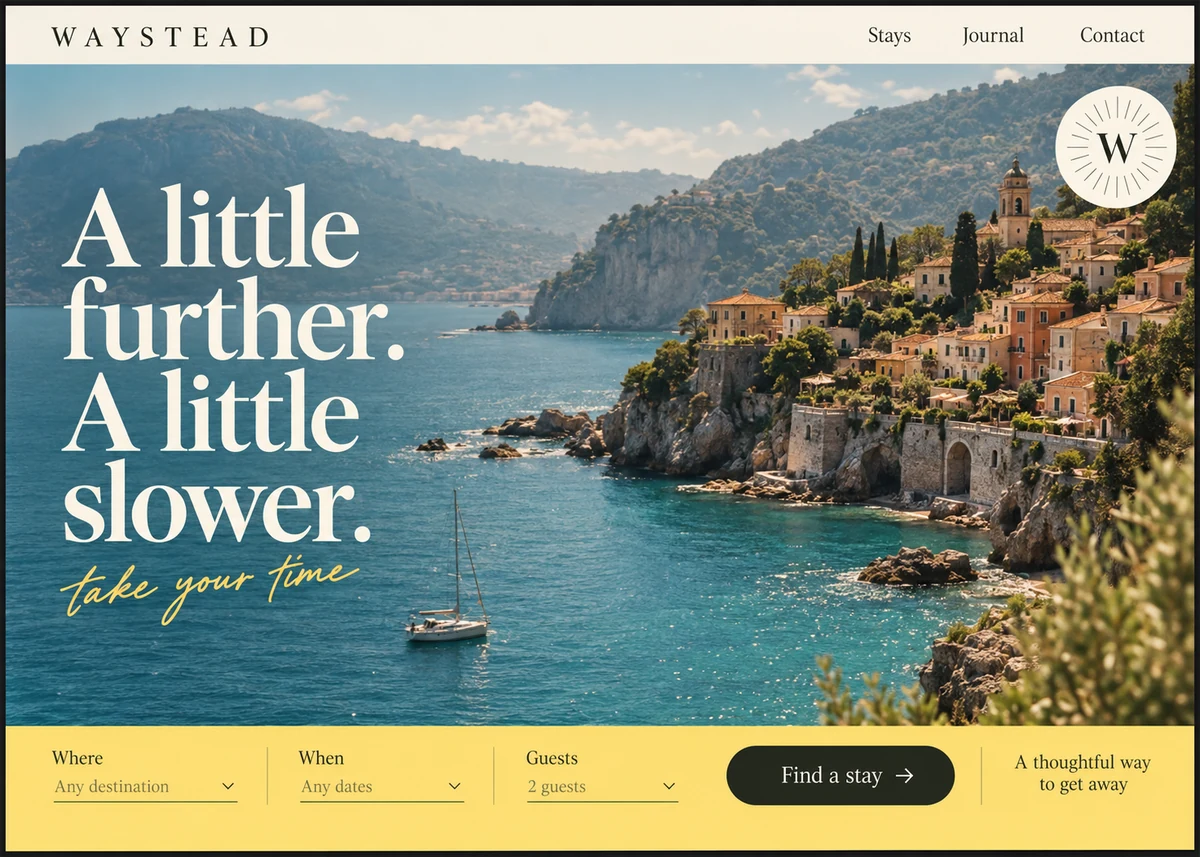
Original AI-assisted designs for fictional brands. These are visual concepts, not client projects or working products.